Evaluating decentralized software frameworks, consensus protocols, and ledger-based networks requires rigorous technical due diligence. As distributed architectures shift from monolithic designs to specialized modular stacks, engineering leaders and system architects face complex trade-offs between execution speed, data availability, settlement finality, and cryptoeconomic security.
Selecting the appropriate foundation for a decentralized application or enterprise network requires looking beyond marketing claims. It demands a systematic evaluation of underlying protocol mechanics, operational risks, security guarantees, and long-term maintainability.
Core Evaluation Criteria
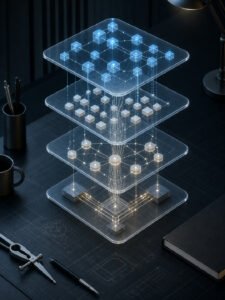
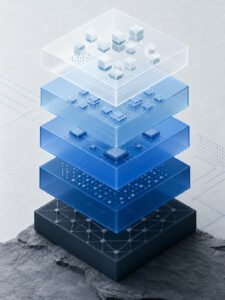
Assessing decentralized software environments requires evaluating multiple interdependent layers: consensus stability, cryptographic security, developer ergonomics, and governance models.
+-------------------------------------------------------------+
|                     Application Layer                       |
|        (Account Abstraction, Smart Contracts, UX)           |
+-------------------------------------------------------------+
|
+-------------------------------------------------------------+
|                      Execution Layer                        |
|       (Parallel VMs, Zero-Knowledge / Optimistic Rollups)   |
+-------------------------------------------------------------+
|
+-------------------------------------------------------------+
|                  Data Availability Layer                    |
|             (Erasure Coding, Sampling Proofs)               |
+-------------------------------------------------------------+
|
+-------------------------------------------------------------+
|               Consensus & Settlement Layer                  |
|     (Proof-of-Stake, Finality Gadgets, Cryptoeconomics)     |
+-------------------------------------------------------------+
Cryptoeconomic Security and Consensus Robustness
The baseline viability of any distributed ledger depends on its security model. When reviewing proof-of-stake or hybrid consensus networks, teams must analyze the total value securing the network and the distribution of validating nodes:
- Validator Distribution and Nakomoto Coefficient: The minimum number of independent entities needed to collude to stall or rewrite the ledger provides a direct metric of decentralization. Networks where a handful of staking pools or hosted infrastructure providers control more than a third of the active stake present systemic platform risk.
- Finality Mechanics: Systems vary significantly between probabilistic finality, deterministic single-slot finality, and multi-epoch checkpointing. Mission-critical financial workflows require immediate settlement finality, whereas high-volume social or streaming platforms may tolerate weak subjective finality with optimistic confirmations.
- Slashing and Attack Costs: The economic penalty for validator misconduct must exceed the potential extractable value of an exploit. Reviewing the protocol’s automated slashing mechanisms, unbonding periods, and response to long-range reorganization attacks is essential.
Performance and Scalability Metrics
Throughput claims are frequently exaggerated in promotional benchmarks that measure raw, empty transactions under idealized laboratory conditions. Evaluation frameworks must prioritize realistic performance metrics:
- Sustained Transactions Under Complex State Access: Raw transaction-per-second (TPS) figures are meaningless without measuring execution complexity. Benchmarks must assess transactions that read and write to shared storage, such as decentralized exchanges or shared state registries.
- Megagas per Second (MGas/s): Computational throughput is best measured by the volume of gas or execution units processed per second, reflecting actual smart contract load rather than simple balance transfers.
- State Growth and Hardware Footprint: High computational throughput often accelerates state bloat. If validating nodes require enterprise-grade memory and NVMe arrays to maintain the current state, running independent validators becomes cost-prohibitive, leading to centralization.
Developer Ecosystem and Tooling Maturity
A protocol’s long-term viability correlates with developer retention, testing infrastructure, and tool reliability:
- Execution Environment Compatibility: Support for established virtual machines—such as EVM, Wasm-based runtimes, or modern parallelized environments—determines how easily existing development teams can onboard. Tooling maturity for debugging, local environment simulation, and continuous integration significantly affects development velocity.
- Client Diversity: Production networks dependent on a single client implementation face systemic single-point-of-failure risks. Stacks with multiple independently maintained client implementations written in different languages demonstrate higher resilience against zero-day compiler and logic bugs.
- Formal Verification Support: Protocols featuring smart contract languages designed with mathematical verification in mind reduce the incidence of reentrancy, integer overflow, and unauthorized state mutation.
Architectural Foundations
The architecture of decentralized protocols has bifurcated into monolithic networks and modular systems. Understanding this distinction is essential when mapping a project’s needs to an infrastructure provider.
Monolithic Versus Modular Stacks
Monolithic architectures handle execution, consensus, settlement, and data availability within a single native node network. This design simplifies state management, preserves atomicity across all transactions, and eliminates cross-layer communication latency. However, it forces every validator to scale all hardware components simultaneously, creating an upper bound on performance before decentralization degrades.
Modular architectures decouple these functions into specialized layers:
- Execution Environments: Rollups, sidechains, and off-chain execution runtimes process transactions and state updates independently, posting proofs or compressed transaction data back to a base layer.
- Settlement and Dispute Resolution: A shared base layer provides an authoritative dispute resolution framework and settles balances across execution layers.
- Data Availability (DA): Dedicated DA networks ensure that the transaction data necessary to reconstruct the current execution state is publicly accessible, often utilizing erasure coding and data availability sampling.
- Shared Sequencer Networks: Independent clusters of sequencers coordinate transaction ordering across multiple rollups to provide atomic execution and reduce cross-domain maximal extractable value (MEV).
Execution Engines and State Models
Modern decentralized virtual machines balance backwards compatibility with parallel execution:
- Parallelized Virtual Machines: Traditional execution environments process state transitions sequentially, creating severe bottlenecks during periods of high demand. Modern execution runtimes utilize software transactional memory or access-list declarations to run non-conflicting state changes across multi-threaded architectures.
- Zero-Knowledge Verifiers: Validity-proof-based environments compile execution traces into succinct cryptographic proofs. This allows low-specification client nodes or base layer contracts to verify state changes without re-executing the underlying transactions.
- Object-Centric vs. Account-Centric Models: Account-based architectures track global state through updated balances and storage roots. Object-centric architectures treat assets and contract logic as discrete, addressable objects with explicit ownership models, making concurrent execution easier to schedule.
Implementation and Integration Workflows
Deploying infrastructure or launching contracts on a decentralized network requires a disciplined integration pipeline. The process transitions from node provisioning to rigorous automated verification.
+--------------------------------------------------------------+
| 1. Infrastructure Provisioning                               |
|    - RPC endpoint configuration & redundancy                 |
|    - Private key isolation & HSM integration                 |
+--------------------------------------------------------------+
|
v
+--------------------------------------------------------------+
| 2. Smart Contract Development & Testing                      |
|    - Local sandbox deployment (Deterministic fork tests)     |
|    - Static analysis, fuzzing, & formal verification         |
+--------------------------------------------------------------+
|
v
+--------------------------------------------------------------+
| 3. Testnet Validation & Security Audits                      |
|    - Long-running multi-client staging deployments           |
|    - Third-party independent threat modeling                 |
+--------------------------------------------------------------+
|
v
+--------------------------------------------------------------+
| 4. Mainnet Deployment & Monitoring                           |
|    - Multi-signature contract initialization                 |
|    - Automated circuit breakers & real-time telemetry        |
+--------------------------------------------------------------+
Infrastructure Provisioning
Integrating with decentralized networks begins with establishing reliable network interfaces:
- Node Operations and RPC Redundancy: Production applications must avoid relying on single public remote procedure call (RPC) endpoints. Teams should deploy dedicated, load-balanced full nodes across independent infrastructure providers, supplemented by private read/write RPC relays that mitigate frontrunning.
- Key Management and Signature Workflows: Storing private keys directly within server environments introduces catastrophic compromise vectors. Production setups require Hardware Security Modules (HSMs) or multi-party computation (MPC) key-management services to sign transactions, combined with strict role-based access controls and automated rate limits.
Testing and Security Pipelines
Development workflows must account for the immutability of deployed contracts and the adversarial nature of shared state networks:
- Local Sandboxes and Fork Testing: Developers should test state logic against deterministic, locally hosted network instances that mirror target network state, including contract addresses, token balances, and historical block data.
- Fuzzing and Invariant Testing: Beyond unit testing, smart contracts must undergo property-based fuzzing to uncover edge cases. Fuzzing harnesses generate millions of pseudo-random inputs to verify that core contract invariants (such as token conservation or authorized access) can never be violated.
- Staging Deployments on Public Testnets: Deploying contracts to public, decentralized testnets helps identify issues with block-time variability, gas price volatility, and uncoordinated client updates before mainnet deployment.
Production Monitoring and Fail-Safe Mechanics
Once deployed, applications require continuous telemetry to detect anomalies:
- Mempool and Event Monitoring: Real-time listeners should monitor both pending mempool transactions and finalized event logs to identify suspicious state changes, anomalous arbitrage loops, or sudden transaction reverts.
- Automated Circuit Breakers: Mission-critical contracts should feature pause mechanisms controlled by multi-signature configurations or automated anomaly-detection bots. These safeguards temporarily freeze deposits, withdrawals, or liquidations if abnormal activity is detected.
Practical Use Cases and Architectural Fit
Different deployment scenarios require distinct infrastructure trade-offs. Selecting a stack involves matching performance profiles, privacy requirements, and trust assumptions to the specific domain.
Enterprise Settlement and Tokenized Assets
Financial asset issuance requires legal compliance, predictable finality, and zero tolerance for chain reorganizations:
- Preferred Architecture: High-security settlement layers with deterministic finality, or application-specific rollups managed by a known validator set.
- Key Requirements: Granular identity controls (such as integrated account abstraction with identity registries), native token standards supporting pause and freeze functions, and audit-friendly data logging.
- Trade-Offs: Sacrificing permissionless validator participation in exchange for high regulatory clarity and guaranteed transaction priority.
High-Frequency Consumer Applications
Social networks, community platforms, and interactive media require micro-transactions and near-instant feedback loops:
- Preferred Architecture: High-throughput modular execution layers or application-specific sidechains backed by dedicated, cost-effective data availability networks.
- Key Requirements: Negligible transaction fees (sub-cent thresholds), transaction batching, and gas sponsorship where developers pay transaction costs on behalf of users.
- Trade-Offs: Weakened underlying cryptoeconomic security or reliance on centralized sequencers in exchange for high responsiveness and frictionless onboarding.
Verifiable Off-Chain Compute and Oracle Networks
Applications relying on heavy machine learning inference, real-world data ingest, or off-chain data processing require verification rather than raw on-chain execution:
- Preferred Architecture: Off-chain compute clusters that generate zero-knowledge or optimistic validity proofs, verified on an established settlement layer via lightweight smart contracts.
- Key Requirements: Cryptographic libraries capable of verifying zero-knowledge SNARKs or STARKs efficiently, coupled with multi-source oracle aggregators.
- Trade-Offs: Higher architectural complexity and computational latency for generating proofs off-chain, offset by minimal on-chain gas costs.
Technical Advantages and Operational Constraints
Operating decentralized software stacks introduces systemic trade-offs between resilience and developer flexibility.
المزايا
- Trust-Minimized Auditability: Unlike traditional database architectures where root administrators possess unilateral data mutation rights, decentralized ledgers enforce state transitions via transparent, immutable cryptographic rules.
- قابلية التركيب: Smart contracts on shared execution layers function as open application programming interfaces that can interact atomically within a single transaction. This enables complex multi-protocol workflows without bespoke integration agreements.
- Censorship Resistance and Redundancy: By distributing state across geographically and jurisdictionally diverse nodes, networks gain high fault tolerance against localized infrastructure outages, targeted network filtering, and operator insolvency.
Operational Constraints
- Deterministic Latency Ceilings: Distributed consensus mechanisms inevitably introduce state propagation and confirmation delays. They cannot match the sub-millisecond latencies delivered by centralized relational databases or proprietary memory caches.
- Data Immutability Risks: The inability to easily rewrite state means software defects, logic vulnerabilities, and data corruption cannot be remedied via simple database updates. Fixing broken contracts requires complex proxy patterns, governance approvals, or complete system migrations.
- MEV and Frontrunning Vulnerabilities: Publicly visible mempools expose users to frontrunning, transaction reordering, and sandwiching by predatory searcher bots. Preventing this value extraction requires implementing specialized commit-reveal schemes, private transaction relays, or threshold encryption.
Decision Matrix and Strategic Selection Framework
To systematically determine which network architecture fits a target deployment, organizations can evaluate their operational parameters across five critical vectors:
| Selection Criteria | Enterprise Settlement | High-Frequency Consumer | Verifiable Compute |
|---|---|---|---|
| Throughput Requirement | Low to Moderate (< 100 TPS) | Ultra-High (> 2,000 TPS) | Low on-chain, High off-chain |
| Finality Tolerance | Strict Deterministic (< 5 seconds) | Optimistic / Near-Instant (< 1 second) | Flexible, Proof-dependent |
| Data Privacy Needs | Confidential State / Zero-Knowledge | Public / Pseudonymous | Private off-chain state verification |
| Gas Fee Tolerance | Moderate to High ($0.10 – $2.00+) | Negligible / Gasless (< $0.001) | Low verification overhead |
| Decentralization Priority | High settlement layer security | Medium (Optimized for performance) | High verification immutability |
Application-Specific versus Shared Execution Layers
A foundational architectural decision is whether to deploy on a shared general-purpose network or build a dedicated application-specific rollup or chain:
Deploy on a Shared Network When:
- Your protocol relies on immediate liquidity integration and atomic composability with external smart contracts.
- Your engineering team prefers to focus entirely on application logic without managing sequencers, validators, bridge infrastructure, or RPC nodes.
- Capital constraints prevent bootstrapping an independent validator set or leasing dedicated sequencer throughput.
Deploy an Application-Specific Layer When:
- Your application generates high, unpredictable transaction volumes that could cause gas spikes or congest an entire shared network.
- You require customized state execution rules, non-standard transaction ordering logic, or gas fees paid in native application tokens.
- Your governance or compliance requirements demand fine-grained control over which nodes can participate in block production or validation.
Selecting a Web3 project, layer, or developer framework requires matching system-level needs to protocol mechanics. By applying structured criteria that weigh consensus security, virtual machine efficiency, operational tooling, and economic overhead, engineering teams can build resilient decentralized architectures that support long-term production requirements.