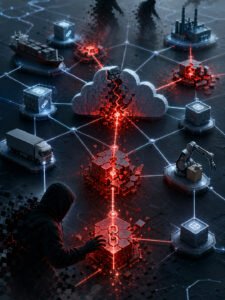
In the dynamic landscape of cybersecurity, the emergence and rapid evolution of Web3 technologies have introduced both innovative opportunities and complex challenges, particularly within the realm of cloud supply chain security. As of 2026, a comprehensive analysis by Unit 42 underscores how Web3’s decentralized nature, coupled with its foundational elements like blockchain, smart contracts, and decentralized applications (dApps), is increasingly being exploited by threat actors. This report delves into the intricate ways Web3 principles are being weaponized, from enhancing traditional attack vectors to creating entirely new avenues for exploitation, thereby complicating the defensive strategies for organizations relying on cloud infrastructure.
The core challenge stems from Web3’s paradigm shift towards decentralization, aiming to reduce reliance on centralized entities. While this promises greater transparency and user control, it simultaneously creates new vulnerabilities when mishandled or targeted maliciously. Threat actors are demonstrating a growing sophistication in leveraging these characteristics, moving beyond conventional phishing and malware distribution to more insidious methods that exploit the very architecture of Web3 within cloud environments.
The Interplay of Cloud, Supply Chain, and Web3 Vulnerabilities
The convergence of cloud computing, supply chain dynamics, and Web3 technologies creates a particularly fertile ground for advanced cyber threats. Cloud supply chains, encompassing a vast network of third-party services, APIs, and open-source components, are inherently complex and present numerous points of entry for attackers. The integration of Web3 elements into these supply chains, whether for data integrity, identity management, or decentralized finance (DeFi) operations, inadvertently extends the attack surface.
Unit 42’s research highlights several critical areas where this interplay manifests:
1. Enhanced Anonymity and Obfuscation: The pseudonymous nature of many blockchain transactions and decentralized networks provides threat actors with an unprecedented level of anonymity. This significantly complicates attribution efforts, allowing attackers to orchestrate sophisticated campaigns, transfer illicit gains, and maintain persistent access without readily traceable digital footprints. Cloud-based command-and-control (C2) infrastructure, when coupled with Web3’s anonymity features, can become exceptionally resilient to takedown attempts.
2. Smart Contract Exploits: Smart contracts, self-executing agreements with the terms directly written into code, are a cornerstone of Web3. While designed for trustless execution, vulnerabilities in their code—such as reentrancy bugs, logic errors, or improper access controls—can be devastating. Attackers are increasingly targeting smart contracts deployed within cloud-hosted Web3 projects, leading to direct financial losses, data manipulation, or the unauthorized execution of functions that compromise the broader cloud supply chain. Such exploits can trigger cascading failures across interconnected decentralized applications and traditional cloud services.
3. Decentralized Application (dApp) Vulnerabilities: dApps, which run on decentralized networks, often interact with traditional cloud services for frontend hosting, data storage, or off-chain computations. Security flaws in dApp code, misconfigurations of underlying blockchain nodes, or compromises of the bridges connecting dApps to conventional web infrastructure provide vectors for attack. These vulnerabilities can be leveraged to inject malicious code into frontends, steal credentials, or manipulate data feeds, thereby impacting the integrity of the cloud supply chain.
4. Supply Chain Injection via Web3 Components: Open-source software (OSS) and third-party libraries are ubiquitous in modern software development, including Web3 projects. Threat actors have become adept at injecting malicious code into these components. When compromised Web3 libraries or SDKs are integrated into cloud-native applications or infrastructure, they can serve as backdoors for pervasive supply chain attacks. This could lead to the compromise of development environments, continuous integration/continuous deployment (CI/CD) pipelines, or even the deployment of tainted images to production cloud environments.
5. Exploitation of Cross-Chain Bridges and Oracles: The nascent Web3 ecosystem relies heavily on cross-chain bridges to enable interoperability between different blockchains and oracles to feed real-world data into smart contracts. Both are critical but often present significant security weak points. Exploiting vulnerabilities in these components can result in massive financial losses, data poisoning, or the unauthorized movement of assets, impacting any cloud services reliant on their integrity. A compromised oracle, for instance, could feed manipulated data to smart contracts, leading to erroneous actions within a cloud-hosted DeFi application.
Case Studies and Observed Trends
Unit 42’s analysis highlights several observed trends and hypothetical scenarios mirroring real-world incidents, illustrating the evolution of these attacks. While specific company names are omitted to maintain focus on the technical aspects, the patterns reveal a clear trajectory:
- Credential Harvesting via Malicious dApp Frontends: Threat actors are creating convincing but fraudulent dApp frontends hosted on cloud infrastructure. Users interacting with these deceptive interfaces unknowingly authorize malicious smart contract calls or provide their wallet private keys, leading to asset theft. The anonymity of Web3 makes it challenging to trace stolen funds.
- Infrastructure-as-Code (IaC) Compromises in Web3 Deployments: Cloud-native Web3 projects often utilize IaC tools (e.g., Terraform, CloudFormation) for deploying blockchain nodes, smart contracts, and associated cloud services. A compromise of IaC repositories or CI/CD pipelines can allow attackers to inject malicious code, deploy backdoored nodes, or reconfigure cloud resources to exfiltrate data or facilitate further attacks.
- Open-Source Library Poisoning for Web3 SDKs: Malicious actors contribute tainted code to popular open-source libraries used in Web3 development kits (SDKs). When these SDKs are integrated into enterprise applications or cloud services, they introduce vulnerabilities or backdoors. This supply chain attack can affect numerous downstream users without their immediate knowledge.
- Decentralized Autonomous Organization (DAO) Governance Exploits: While not directly a cloud supply chain attack in the traditional sense, DAOs often control significant treasuries and protocol parameters. Exploits targeting DAO governance mechanisms (e.g., flash loan attacks manipulating voting power, social engineering) can lead to unauthorized changes that impact cloud-hosted infrastructure, such as reconfiguring access to cloud resources or draining funds from cloud-based multi-signature wallets.
Mitigating the Evolving Threat Landscape
Addressing the evolving threat landscape requires a multi-faceted approach that integrates traditional cloud security best practices with Web3-specific considerations. Unit 42 emphasizes the need for proactive security measures across the entire development and deployment lifecycle.
1. Secure Development Lifecycle (SDL) for Web3 Components:
Incorporating security from the initial design phase of smart contracts and dApps is paramount. This includes rigorous code audits by independent security firms, formal verification methods for critical smart contracts, and comprehensive unit and integration testing. Developers must also be educated on common Web3 vulnerabilities and secure coding practices specific to blockchain environments.
2. Enhanced Supply Chain Visibility and Trust:
Organizations must gain deeper visibility into their entire cloud supply chain, including all third-party dependencies, open-source components, and Web3 libraries. This entails using software composition analysis (SCA) tools to identify known vulnerabilities in dependencies, ensuring regular patching and updates, and establishing robust vetting processes for all third-party integrations, especially those involving Web3 protocols. Trust should be established not just for code, but also for the provenance and integrity of deployed Web3 assets.
3. Robust Identity and Access Management (IAM):
Strong IAM practices remain fundamental. For Web3, this extends to secure management of cryptographic keys, multi-factor authentication for administrative access to cloud resources and Web3 platforms, and implementing the principle of least privilege. Organizations should consider decentralized identity solutions where appropriate, but with careful security considerations.
4. Continuous Monitoring and Threat Detection:
Real-time monitoring of cloud infrastructure and Web3 interactions is crucial. Security Information and Event Management (SIEM) and Extended Detection and Response (XDR) solutions should be configured to detect anomalous behavior, suspicious transactions on blockchain networks, and indicators of compromise (IoCs) related to Web3 exploits. This includes monitoring smart contract events, API calls, and resource utilization for any deviations from baseline.
5. Incident Response and Recovery Planning:
Organizations must have well-defined incident response plans tailored to both cloud and Web3 incidents. This includes protocols for managing smart contract exploits, responding to credential compromises affecting blockchain wallets, and recovering from data integrity issues caused by manipulated decentralized data. Regular drills and simulations are essential to ensure readiness.
6. Bridging Security Gaps Between Traditional and Decentralized Systems:
The interaction points between Web2 (traditional internet) and Web3 components are often vulnerable. Secure API gateways, robust authentication mechanisms for inter-system communication, and careful validation of data passed between centralized and decentralized systems are critical to prevent data poisoning or unauthorized access.
7. Regulatory Compliance and Best Practices:
Staying abreast of evolving regulatory frameworks for Web3 and digital assets is essential. Compliance with data protection regulations, anti-money laundering (AML) guidelines, and other relevant standards helps mitigate legal and financial risks while often enforcing a baseline of security best practices. Adopting industry-recognized security frameworks (e.g., NIST, ISO 27001) and extending them to Web3 operations provides a structured approach to risk management.
The Path Forward
The integration of Web3 into enterprise cloud environments and supply chains is an ongoing process, driven by the promise of innovation, transparency, and efficiency. However, this progress is inherently linked to a growing sophistication in cyber threats. As Web3 technologies mature and become more deeply embedded in critical infrastructure, the attack surface will only expand.
Unit 42’s analysis serves as a stark reminder that security cannot be an afterthought. For organizations navigating this complex landscape, a proactive, adaptive, and holistic security strategy is indispensable. This strategy must seamlessly integrate cloud security best practices with an in-depth understanding of Web3’s unique architectural nuances and potential vulnerabilities. Only through such an integrated approach can organizations hope to harness the transformative potential of Web3 while effectively defending against its evolving risks within the cloud supply chain. The coming years will undoubtedly witness further innovation in both Web3 and the methods used to exploit it, making continuous vigilance and adaptation the hallmarks of robust cybersecurity.